Proxy Anonymity Levels
Proxy anonymity levels describe how much a proxy reveals about the original client and its own role when it forwards an HTTP request. The familiar categories are transparent, distorting, anonymous, and elite. For today's mainstream paid proxy services used in scraping, automation, and access from a chosen location, elite or high anonymity behavior is the normal offering.
The Proxy Services guide places anonymity alongside network type, location, protocols, and other properties of a proxy service. These properties answer different questions. An anonymity label describes particular disclosures in the request; the network and service behind the exit IP determine much of what the customer can actually do with it.
Anonymity in the current proxy market
People buy proxies to send requests through a different IP address. For a price monitor, advertising check, or browser session, passing the original home or server IP to the destination would defeat an important part of that purchase. Adding an obvious proxy marker also gives the website an avoidable signal about the connection. Modern commercial providers have largely converged on removing those disclosures as standard behavior.
High anonymity is available across datacenter, ISP, residential, and mobile services. It can be included in a low-cost package of shared server addresses or a more expensive service with exclusive addresses and stable sessions. The same anonymity behavior can therefore appear in products with very different prices and results.
This changes how the traditional categories should be read. A modern buyer usually chooses the source of the IPs, geography, pool size, rotation, and service limits. Elite behavior is normally included in that choice. Transparent, distorting, and traditional anonymous modes have little relevance as competing paid options for customers who need both their original address and explicit forwarding markers kept out of requests.
The older categories still explain terminology in proxy lists, tests, and documentation. Some also describe deliberate behavior in managed networks. Their continuing existence does not make all four equally useful products for today's proxy customer.
What the four levels reveal
A website receives two kinds of information that must be kept separate. The network connection has a source IP: when the proxy connects to the destination, this is the proxy's exit address. An ordinary HTTP request can also carry headers, which are fields of information sent with the request. A header can contain another address or identify an intermediary.
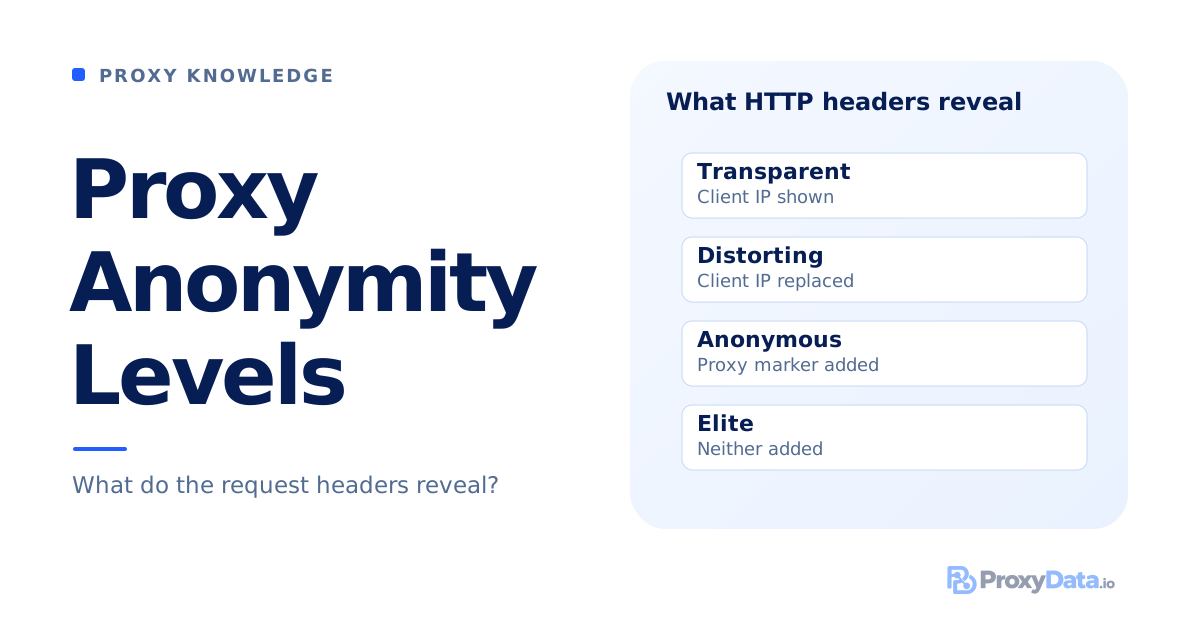
In the diagram, the client's public IP is 198.51.100.24, and the proxy's exit IP is 203.0.113.80 in every row. The distorting example inserts 192.0.2.55 into a header. That false value changes information inside the request; the connection still comes from 203.0.113.80.
The table follows the four HTTP examples shown above. These labels are descriptive market terms, rather than four official grades defined by the HTTP protocol.
| Category | Client address in HTTP headers | Explicit proxy marker |
|---|---|---|
| Transparent | Real client IP | Present |
| Distorting | False client IP | Present |
| Anonymous | Client IP omitted | Present |
| Elite | Client IP omitted | Absent |
Transparent proxies
Transparent Proxies disclose the original client address in the forwarded request, commonly through a field such as X-Forwarded-For. The destination can receive both the proxy exit IP and the address behind it. That does not meet the privacy requirement of a customer paying to keep the original IP out of the website's view.
Within a managed network, identifying the original client can be intentional. Logging and access policies may need that information. The same behavior can serve an administrator's purpose while being unsuitable for the buyer described here. The word “transparent” also has a separate meaning in network interception; the child article explains the distinction.
Distorting proxies
Distorting Proxies replace the client address in a forwarding header with a false value. In the diagram, the website receives X-Forwarded-For: 192.0.2.55, while the actual connection still arrives from 203.0.113.80.
The false header has no power to move the network connection to a different IP. It cannot clear a restriction on the real exit address, change that address's network owner, or erase its history. A destination can also disregard a client-supplied forwarding field. For modern proxy customers, this is an ineffective way to address those restrictions.
Anonymous proxies
Anonymous Proxies, in the traditional classification, omit the original IP but retain an explicit sign of an intermediary, such as Via. They provide IP privacy while openly leaving evidence of forwarding. At a website that rejects requests on that evidence, this mode fails the requirement.
Product descriptions sometimes use “anonymous proxies” more broadly to mean proxies that provide privacy. Such a product may deliver elite behavior. The wording on a sales page and the narrower category reported by a header checker are not always the same thing.
Elite proxies
Elite Proxies, also called high anonymity proxies, omit the original client address and add no explicit proxy marker in the illustrated request. This is the combination normally offered by modern paid services serving privacy, scraping, and automation customers.
The benefit is direct: the proxy avoids handing the destination those additional disclosures. The exit address remains visible, and the website can still evaluate it. An elite result establishes the header behavior; access to a particular website also depends on the address and the request using it.
Cloudflare, Akamai, and PerimeterX
Modern website protection can reject a request before the requested page is served. An explicit proxy marker can be enough to trigger a configured blocking rule. A customer using an anonymous or distorting proxy can therefore receive an immediate refusal even though the original IP is hidden or replaced in a header.
The action depends on the website's policy and the detection that fired. There is no common rule across Cloudflare, Akamai, and PerimeterX that automatically blocks every request containing any hint of a proxy. Forwarding headers also have legitimate uses in corporate gateways and website infrastructure.
Cloudflare evaluates request headers, session characteristics, and browser signals when estimating whether traffic is automated. Website operators can use the resulting assessment to allow, challenge, or block requests.
Akamai Bot Manager describes checks for header anomalies, mismatches between browser claims and request behavior, and other signs of automation. Its detection methods feed the actions configured for the protected site.
PerimeterX/HUMAN Bot Defender considers network reputation, automation signatures, browser behavior, request volume, and application policies. Detecting a signal and deciding to block are related parts of the system, with controls for enforcement.
HUMAN even lists residential IP usage among the capabilities of detected bots. That address type can still appear in traffic the system identifies as automated.
These systems give a practical reason to avoid unnecessary proxy disclosures. If a site's rule rejects the explicit marker left by an anonymous or distorting proxy, elite behavior addresses that particular problem. It does not automatically satisfy rules about IP reputation, request patterns, or the browser making the request.
A blocked exit IP stays blocked
Consider a site protected by Cloudflare with a rule rejecting the address 203.0.113.80. Your proxy connects from that address. A distorting configuration inserts the false value 192.0.2.55 into X-Forwarded-For, but Cloudflare still receives the connection from 203.0.113.80. The change inside the header cannot remove the rule's match on the connecting IP.
Switching the same exit to elite behavior removes the extra forwarding information. The IP restriction still applies. Conversely, if the only matching rule rejected an explicit proxy header, removing that header could change the outcome of that rule. The reason for the refusal determines which change matters.
This is why an anonymity upgrade and an improvement in access can have different results. High anonymity removes avoidable disclosures. A suitable exit address and acceptable request behavior are still needed for the target website.
What an anonymity checker actually tests
A typical header checker receives a test request and examines what arrived. It may identify a client-IP field, a forwarding marker, or the absence of both. The result describes the traffic delivered to that test endpoint through the tested configuration.
A website can identify the same exit IP through a database or its own request history. It does not need your original IP to decide that an address belongs to a proxy network. A result of “Elite” from a header checker and “Proxy detected” from an IP intelligence service can therefore both be correct.
The word “anonymous” also leaves open who is supposed to remain unaware of what. A destination may not know your home IP, while still recognizing the proxy address. If you sign into an account, the website can identify that account regardless of which address carries the session. These are different questions, and the four header categories answer only part of them.
An elite result is useful evidence that the tested request avoided certain disclosures. It is not a measurement of the address's previous use, exclusive ownership, speed, or acceptance by every website.
HTTPS and SOCKS
The diagram describes ordinary HTTP, where the forwarding proxy can read and modify request headers. With HTTPS through a normal HTTP CONNECT tunnel, the client and destination establish an encrypted connection through the proxy. Unless the proxy intercepts and decrypts that connection, it cannot insert Via or X-Forwarded-For into the encrypted request.
This reduces the usefulness of applying the old header categories to every modern connection. The absence of forwarding fields inside an HTTPS tunnel is an expected consequence of how the connection works. It does not demonstrate that the proxy's exit IP is unknown to the destination.
SOCKS also relays application traffic without defining HTTP forwarding headers as part of its protocol. That makes it different from an HTTP proxy that actively rewrites a plain HTTP request. SOCKS does not itself promise encrypted application traffic or acceptance by a protected website. An application can also send identifying information of its own through either kind of proxy.
The destination still receives the exit IP whether the application uses plain HTTP, an HTTPS tunnel, or a SOCKS connection. This remains the address available for network classification and IP-based access rules.
What matters when buying proxies now
For the modern commercial buyer, high anonymity is a normal starting requirement. Once it is included, the meaningful differences move to the addresses and service that accompany it.
A price-monitoring project may need many usable exits and enough capacity to collect pages at the required rate. Repeatedly buying packages with the same “Elite” label will not help if the exits share the same restrictions on the target website.
A browser session that needs a stable address depends on the provider's session model. A rotating pool and a fixed address can both provide high anonymity, but they behave differently when a connection is renewed. The label does not tell the buyer how long an exit can be kept.
For advertising checks or localized content, the exit's geography and the destination's interpretation of that geography matter. For work using shared addresses, other customers can affect limits applied to the same IP. An expensive and a cheap product can pass the same header test while differing substantially on these points.
The traditional classification remains useful for understanding what a request discloses. In today's paid proxy market, elite behavior is the expected privacy baseline. The value of the purchase comes from receiving suitable IPs, the required sessions and capacity, and a service that performs the intended work.