Transparent Proxies
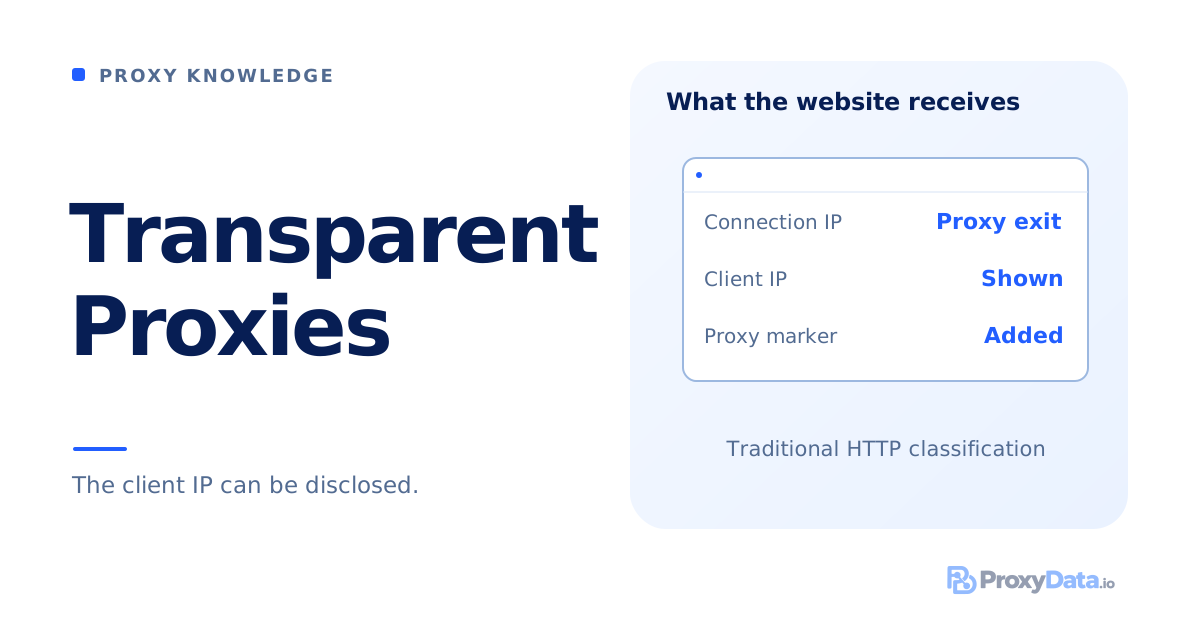
A transparent proxy, in the traditional classification of proxy anonymity, allows the destination website to learn the client's IP address. It can do this by including that address in an HTTP request header. The traffic passes through a proxy, but the client's address is still disclosed.
The broader guide to Proxy Anonymity Levels explains how this differs from anonymous, distorting, and elite proxies. Here, “transparent” describes the information exposed to the destination.
For someone buying a proxy to hide their own IP from websites, that behavior defeats the purpose. A different exit address offers little privacy if the request also tells the website where the client connected from. Transparent proxies make more sense in systems designed to manage traffic and preserve information about its source.
How the website learns your IP
Consider an ordinary HTTP request using example addresses. Your public IP is 198.51.100.24, and the proxy connects to the website from 203.0.113.80. At the network connection level, the website sees the proxy's address.
The proxy also forwards this header:
X-Forwarded-For: 198.51.100.24The website now has both addresses: the proxy's IP from the connection and your IP from the request. An IP display page that reports only the connection address could show the proxy IP even though another part of the request reveals yours.
The header is a statement about the client, rather than a second network connection. A website may ignore statements received from an untrusted sender, but the address has still reached it. Whether the website believes or uses the value does not undo that disclosure.
A separate header, such as Via, can describe a forwarding intermediary. Revealing that a proxy handled the request and revealing the client's IP are two different pieces of information. The defining problem here is the second one.
Why a proxy might preserve the client address
Proxies serve purposes beyond hiding an IP. An organization may use them to apply web access rules, filter requests, or cache suitable responses. In a controlled chain of systems, passing along the client's address can help a downstream application associate a request with its source.
That can be deliberate behavior. The organization wants its systems to retain useful information about the request, while a customer buying a proxy for privacy wants to limit what reaches an outside website. The same behavior has very different value in those two settings.
Another meaning of “transparent”
Network administrators also use “transparent proxy” to describe traffic interception. In that setup, the network directs traffic through a proxy without the user entering a proxy address in the browser or application.
This describes how traffic reaches the proxy. The anonymity classification describes what information the proxy passes onward. These properties are independent: entering a proxy manually does not guarantee that it hides your IP, and automatic interception alone does not tell you which headers a website receives.
This distinction explains why a technical description of a transparent network gateway may appear to discuss a different product from a proxy list using the same word.
What changes with HTTPS
The header example above applies to an HTTP request that the proxy can read and forward. With an ordinary HTTPS connection through an HTTP proxy, the client normally establishes a tunnel using CONNECT. The HTTP headers sent to the website then travel inside the encrypted TLS connection.
A proxy carrying that tunnel without decrypting it cannot insert X-Forwarded-For into the protected request. A managed gateway that decrypts HTTPS for inspection is a different arrangement; the client's device must trust the gateway's certificates for that inspection to work without certificate errors.
Consequently, a “transparent” result from a plain HTTP test does not describe every protocol or connection that the same service supports. For a buyer, the useful distinction is whether the destination receives the client's address in the traffic they actually use. A changed connection IP, on its own, is only part of that answer.