Elite Proxies
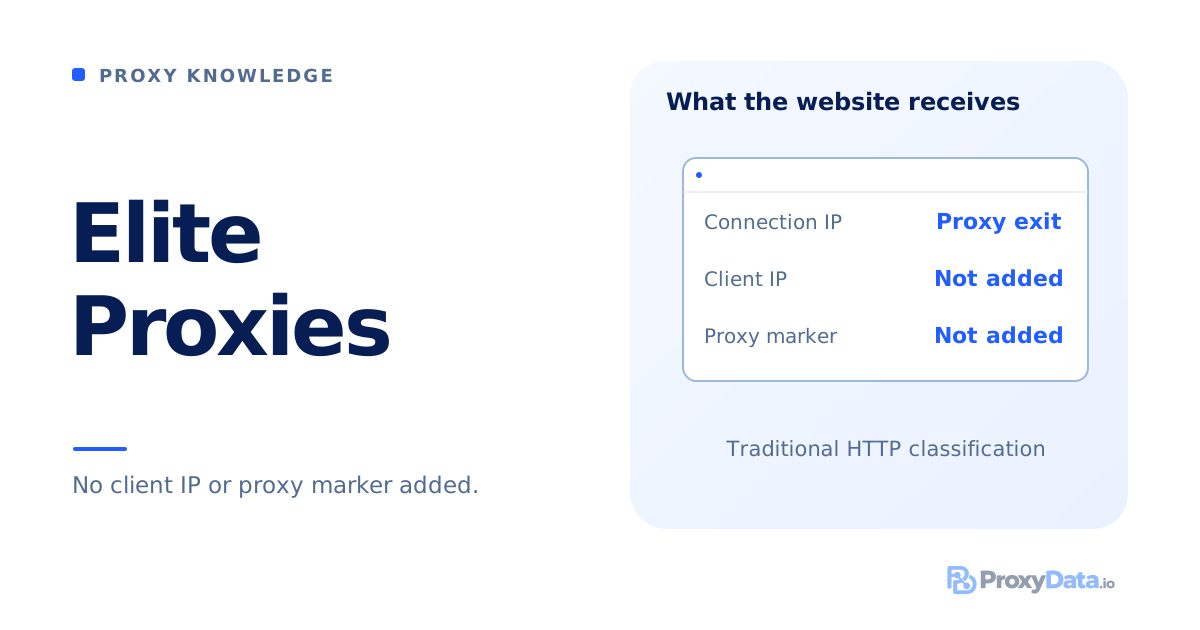
An elite proxy, also called a high anonymity proxy, forwards traffic without disclosing the client's original IP in HTTP headers or adding an explicit proxy marker. For mainstream paid proxy services used for scraping, automation, and location-based access, this has become the standard offering. High anonymity is normally included in the service you buy.
The Proxy Anonymity Levels guide explains the traditional transparent, distorting, anonymous, and elite categories. Of these, elite describes the privacy behavior that today's commercial proxy customer generally receives. The other categories help explain older terminology and test results, but rarely represent competing plans in a modern proxy provider's catalog.
What the website receives
Suppose your public IP is 198.51.100.24 and the proxy's exit IP is 203.0.113.80. The website receives a connection from 203.0.113.80. Your original address is absent from forwarding headers such as X-Forwarded-For, and the proxy adds no explicit intermediary marker such as Via.
This is useful when requests from your home, office, or automation server should reach a website through the purchased exit address. The proxy keeps your original IP out of the forwarded request. Sending that address alongside the replacement would defeat an important reason for buying the service.
Why high anonymity became the commercial default
A customer buying proxies for price monitoring, advertising checks, or browser automation expects the service to keep the original IP private. Adding a header that openly identifies the intermediary also gives the destination an avoidable signal about the connection. Providers serving these customers have therefore largely converged on high anonymity as their normal service behavior.
The older categories leave disclosures that these buyers usually want removed. A transparent proxy passes on the client's IP. An anonymous proxy hides that address but retains an explicit proxy marker. A distorting proxy supplies a false client address in a header, while the destination still receives the connection from the real proxy exit. None of these offers the same combination as elite: keeping the original address private and omitting explicit forwarding markers.
This explains why modern providers usually organize their products around datacenter, ISP, residential, and mobile networks. High anonymity can be provided across all four. A customer commonly chooses an IP source, location, and session model while receiving elite behavior as part of that choice. The word “Elite” may appear on the product page or simply be covered by the service's anonymity description.
Transparent forwarding still has uses in managed networks, where recording the original client can be intentional. For a buyer paying to keep that address private, however, it does not meet the requirement. The commercial context determines why the old categories matter.
Elite proxies and HTTPS
The classic header diagram describes ordinary HTTP. Much of today's web traffic uses HTTPS, where the client and website exchange encrypted requests. With an HTTP proxy, this commonly happens through a CONNECT tunnel. A proxy relaying that tunnel without intercepting TLS cannot insert Via or X-Forwarded-For into the encrypted request sent to the website.
Keeping the client IP out of headers and encrypting the traffic are separate protections. An elite proxy carrying plain HTTP can still read its contents. For HTTPS, the encryption comes from the secure connection between the client and website. This is another reason to understand what the anonymity label measures: a routine encrypted tunnel already prevents the proxy from adding those headers inside the request.
Why an elite proxy can still be blocked
A proxy checker can report “Elite” while your target website refuses the same connection. The checker found no revealing headers. The website can evaluate the exit IP and the activity coming from it.
For example, an address may already be listed in a database as belonging to a proxy or hosting network. It may also have restrictions from previous use. With a shared exit, other customers' traffic can contribute to limits on the same address. None of these requires the website to discover your home IP.
The destination can also assess request frequency, session history, and browser behavior. Removing a forwarding header does not erase those signals. An elite proxy can therefore do its job of keeping the original address private while the site still recognizes the exit as a proxy or rejects the traffic for another reason.
What buyers choose when high anonymity is standard
A low-cost shared datacenter proxy and a more expensive dedicated ISP proxy can both be elite. Their difference in price buys different working conditions. Once high anonymity is included, the useful comparison moves to the properties that determine whether the service suits the task.
| Property | Why it matters to the buyer |
|---|---|
| Exit network and IP history | Datacenter, ISP, residential, and mobile addresses can receive different treatment from the target website; previous use can affect access. |
| Location and available pool | The service needs suitable addresses in the required geography and enough capacity for the workload. |
| Shared or exclusive use | Other customers may use the same exit and contribute to limits applied to that IP. |
| Static or rotating sessions | The address must stay in place or change according to the task. |
| Performance and service terms | Throughput, connection limits, reliability, traffic allowances, and replacement conditions affect everyday work. |
The practical value of elite behavior is straightforward: the proxy avoids disclosing the original IP and adding obvious intermediary markers. That is the normal starting point for a modern paid proxy service. The reasons to choose one provider or pay more lie in the usable addresses, sessions, capacity, and conditions delivered alongside it.