Distorting Proxies
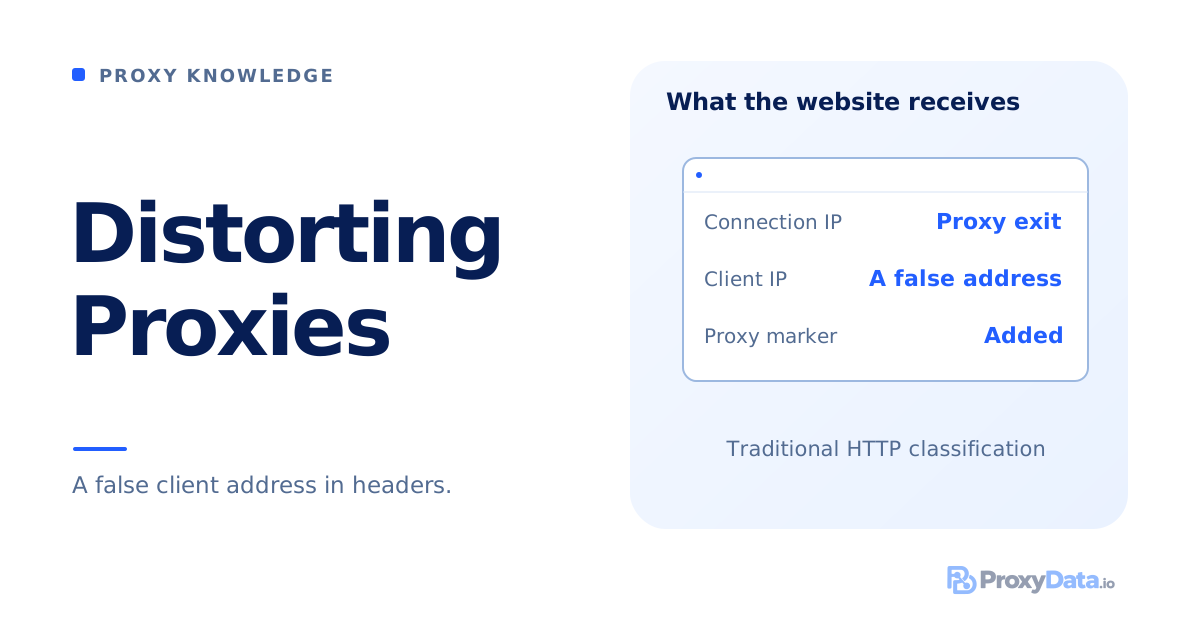
A distorting proxy replaces the client's real IP address with a false address in an HTTP request header. In the traditional anonymity classification, it hides that piece of information while still leaving signs that a proxy handled the request.
The broader guide to Proxy Anonymity Levels places distorting proxies alongside transparent, anonymous, and elite proxies. The distinction concerns what the proxy tells a website about the client.
For a proxy buyer, this is an older classification with limited practical value. Inventing an address does not give the connection a new location or a better reputation. The useful part is keeping the real client IP out of the request; a fabricated replacement adds little when the website has no reason to trust it.
What the proxy changes
Consider a client whose public IP is 198.51.100.24. The proxy connects to a website from 203.0.113.80. Instead of passing along the client's address, it sends a made-up value in X-Forwarded-For, a header used to carry information about the client:
X-Forwarded-For: 192.0.2.55
Via: 1.1 proxy
There are now three addresses in the example. The client's real address stays out of this header. The website receives the connection from 203.0.113.80, while the header claims that the client is 192.0.2.55. That third address is simply text inside the request. The proxy has not connected from it.
The Via line also identifies an intermediary. In this example, the client's address is concealed in the forwarded headers, but the use of a proxy is openly disclosed.
A false address is not a different exit
Suppose a proxy exits through a datacenter in one country. Inserting an address associated with another country into a header does not move that connection. A website that determines location from the connection IP still looks up the actual exit address.
The same distinction applies to rotation. Changing the invented value on every request does not create a new proxy exit. If the service keeps using the same outgoing IP, a destination can still associate those connections with that address. Its network ownership, reputation, and any restrictions applied to it do not disappear because a header contains different numbers.
Why a checker may show the invented IP
An IP-checking page may read a forwarded header and present its value as the visitor's address. Another page may report the connection address instead. The two results can differ even when both requests use the same proxy exit.
Websites decide which sources of client-address information they trust. In a controlled setup, an application can accept such information from its own known gateways. A customer-supplied proxy is not automatically one of those trusted systems. A false address can therefore appear in a checker's output without becoming the address another website uses for access rules or location detection.
The limits of the label
This description applies to HTTP requests that the proxy can read and modify. With ordinary HTTPS through a CONNECT tunnel, the request headers are inside the encrypted connection. A proxy forwarding that tunnel without decrypting it cannot rewrite those headers. A plain HTTP classification does not establish the same behavior for HTTPS or SOCKS traffic.
Distorting also says nothing about the size of the provider's IP pool, the stability of an address, or whether a particular website accepts it. Those properties belong to the proxy service itself. The label describes a false statement in a request; it does not turn that statement into a new network identity.