Blocked Ports
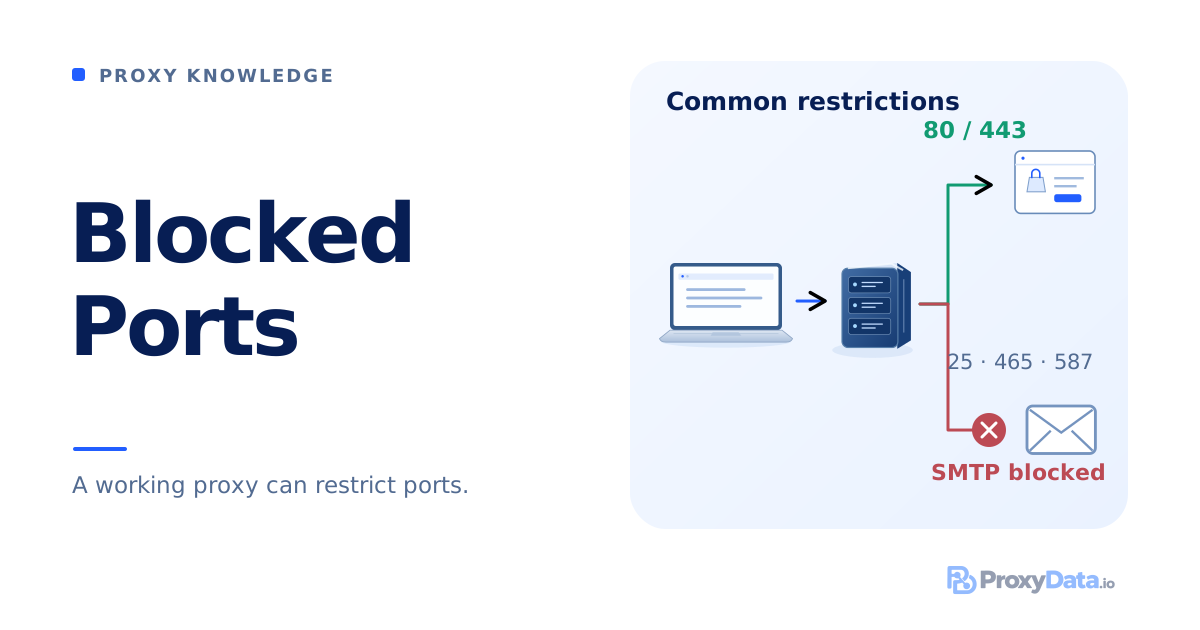
Blocked ports are restrictions on the network services that a proxy can connect to. An IP address and subscription can be fully operational while the service opens an online shop but refuses a connection to a mail server or database.
These restrictions are part of Proxy Usage Limits. They define which connections the product carries. Buying a dedicated address, a larger package, or unlimited traffic does not automatically expand that permission.
A typical example starts with a successful browser test. The customer sees the expected country, opens a mailbox, and assumes email works through the proxy. Sending from a mail application then fails. The first test was successful; it simply tested a different connection.
Connection port and destination port
A port is a number that distinguishes network services on an IP address. A connection depends on the address, the transport—TCP or UDP—and the port number. HTTPS commonly uses TCP 443, while mail submission can use TCP 587.
In the credentials proxy.example:1080, 1080 is the entry port on the proxy. Through that entry point, the application separately requests a connection to its destination: for example, shop.example:443 or mail.example:587. The same proxy can allow the first destination and reject the second.
Changing 1080 to 443 in the proxy settings therefore does not turn a mail connection into a web request. Even if the provider offers an entry point on 443, it still receives the requested destination port.
Some services also use the entry port to select a sticky session or a particular exit IP. Its meaning depends on the product: a number in the purchased proxy list does not describe which external services are available.
SMTP and webmail
Blocking outbound SMTP is normal practice in mass-market commercial proxy networks. Buyers should not assume that sending through ports 25, 465, and 587 is included. Published policies include permanent restrictions with no exceptions, including restrictions that remain after identity verification.
The reason is practical. A single spam campaign creates consequences for the infrastructure carrying it. Complaints reach address owners and network operators; IPs enter sender blocklists; infrastructure suppliers may restrict service. The next customer receives an address with someone else's poor history, while the provider loses useful capacity in its pool.
In a residential network, the consequences can also reach the owner of the connection carrying the traffic. That person did not choose the email recipients, but external systems see their address. Providers can prevent this before the first message is sent by refusing the connection.
| TCP port | Purpose |
|---|---|
| 25 | SMTP relay between mail servers; STARTTLS may be used |
| 587 | Submission from a mail application to a server, commonly with STARTTLS |
| 465 | Submission with TLS from the start of the connection |
| 110 / 995 | POP3 retrieval / POP3 with TLS |
| 143 / 993 | IMAP mailbox access / IMAP with TLS |
Receiving and sending can have separate permissions. Documented commercial products open 110, 143, 993, and 995 after identity verification while leaving SMTP blocked. Other services prohibit all these mail protocols. Encryption on 465 or 993 does not remove the restriction: the destination port is known before any email content is transferred.
Webmail follows a different route. When someone sends a message in a browser, the browser communicates with the mail website over HTTPS. The mail service handles delivery. The customer's mail application is not making a direct SMTP connection through the purchased proxy.
Blocked SMTP can therefore coexist with working Gmail, Outlook, or Yahoo Mail in a browser. Webmail is not guaranteed either: the provider may restrict its domains or login pages, and the mail platform may reject the proxy connection.
An offer of “SMTP through any residential IP, with no checks or restrictions” deserves scrutiny of the network's origin. Proxy services have operated on infected devices whose owners never agreed to sell access to their connections. A lack of controls in such a network is not a quality advantage. An open port alone does not prove that a seller operates a botnet, however: approved access to mail infrastructure and uncontrolled resale of other people's devices are different arrangements.
Other services that may be restricted
Mail ports are the clearest example. Other restrictions depend on the product and the tasks it is designed to support.
| Service | Typical ports | Why access may be restricted |
|---|---|---|
| Remote access | SSH 22, Telnet 23, RDP 3389 | Reducing credential attacks and unauthorized server access |
| Databases and data stores | MySQL 3306, PostgreSQL 5432, Redis 6379, MongoDB 27017 | Reducing attacks on exposed databases and unauthorized data extraction |
| Windows services | RPC 135, NetBIOS 137–139, SMB 445 | Limiting access to file shares and services not intended for arbitrary internet connections |
| DNS | 53; DNS over TLS uses TCP 853 | Controlling access to external resolvers; transport permissions matter separately |
| FTP | TCP 21 for control, plus separate data connections | A product may not support the additional ports and connection directions required |
| Alternative web services | For example, 8080 and 8443 | A service may allow only standard web ports or require separate approval |
| Certain UDP services | For example, SSDP 1900 or Memcached 11211 | Preventing exposed services from being used in reflection attacks with enlarged responses |
These are port assignments and possible reasons for restrictions, not a universal list of banned numbers. An administrator can legitimately connect to their own database or SSH server. The question is whether the chosen proxy product carries that connection.
P2P needs a separate distinction. BitTorrent has no single mandatory port; clients can configure it. The 6881–6999 range found in reference lists does not describe every possible connection. A provider may prohibit the activity, restrict a transport, or apply other network rules. Sustained heavy traffic and complaints about particular shared content explain restrictions; the use of P2P alone does not make a transfer unlawful.
How permission lists work
Some services block selected ports while leaving others available under their general rules. Others allow only the destinations they list. For the second model, 8443 can be unavailable even when it serves an ordinary HTTPS page.
Published conditions show how specific these lists can be. One residential product starts with 80, 443, 5228, 53, and 853. Identity verification adds other numbers, including 8080 and 8443. This is a documented service arrangement, not a standard allowance for every residential proxy.
A rule can depend on the account, plan, network type, or destination. Residential, ISP, datacenter, and different mobile products from one seller can have different permissions. Identity verification opens only the capabilities covered by that process.
Charging by the gigabyte describes how usage is billed. A dedicated IP defines who uses the address. Unlimited traffic describes billing or permitted consumption. None of these characteristics, by itself, promises access to every port.
SOCKS5, HTTPS, and UDP
SOCKS5 can request connections to different TCP ports, and its standard also describes UDP ASSOCIATE. The proxy implementation may not provide UDP, and the service's rules may prohibit particular destinations. A SOCKS5 label does not remove access restrictions.
The same distinction applies to HTTP CONNECT. It establishes a tunnel to the requested address and port; the HTTP standard explicitly recommends limiting unsafe destinations and identifies spam through port 25 as a risk.
That decision does not require HTTPS decryption. The provider knows the requested destination and can reject the connection before any page content is exchanged.
TCP and UDP also need separate treatment. Working HTTPS over TCP 443 does not establish access to UDP 443, which HTTP/3 commonly uses. A browser can fall back from HTTP/3 to HTTP over TCP and still open the website. A game or voice application may have no suitable fallback.
Even successful access by domain name does not prove that UDP 53 is permitted. If the client passes the hostname to the proxy, the proxy can resolve it itself. That is different from carrying the client's DNS query through a UDP proxy.
Restrictions between the client and the destination
The proxy's own rules are only one place where a connection can stop.
For a datacenter product, outbound access also depends on the hosting network. Cloud server suppliers publish their own mail-port restrictions, and their lists differ. One arrangement blocks 25, 465, and 587; another blocks 25 and 465 while permitting 587. Administrator access to a VPS does not grant control over the host's network filters.
Residential proxies add the participant's internet connection. The gateway may accept a request while the exit device's internet provider blocks the required connection. Consumer internet operators also publish restrictions, including SMTP 25 and selected network-service ports. Permission at the central gateway therefore does not establish identical access from every node.
The destination server can also reject connections, accept only approved source IPs, or have no running service on the requested port. An unavailable service and a proxy restriction can look similar to the customer.
Changing exit devices can sometimes change the route and remove a restriction specific to one network. Rotation does not override a product-wide rule: if a destination is prohibited for the account, new IPs remain subject to that restriction.
What error messages mean
There is no single response that every provider uses for a blocked port. Services may return explicit messages, their own additional codes, connection resets, or timeouts.
| Example from published documentation | Meaning in that particular system |
|---|---|
403 PORT_BLOCKED | The requested destination port is prohibited |
407 PORT_NOT_ALLOWED | The selected sticky-session port is not permitted by the plan settings |
HTTP 503 with additional code 503.4.1 | The destination port is denied |
SOCKS5 0x02 | The connection is not allowed by the ruleset |
The first two are easy to confuse. Both contain the word port, but one concerns an external service and the other concerns the customer's proxy access settings.
Standard HTTP 407 indicates that proxy authentication is required. A provider may attach its own explanation of an account problem. Bare 403, 502, 503, or 504 statuses do not identify the cause with enough precision.
The stage of failure matters too. A proxy response rejecting a CONNECT tunnel happens before the request for the website's page. A website response after the tunnel is established belongs to a different stage. An application error that hides those details does not establish that the exit IP has been banned.
When the browser stops the request
Browsers have their own unsafe-port restrictions for HTTP(S). For example, entering https://mail.example:25 can cause a browser to reject the request before contacting the proxy.
That action does not test SMTP: the browser is attempting a web protocol on a mail port. The same distinction matters for browser automation. The client can report a failure even though the provider received no request.
Why an application can work only partly
An application does not necessarily use one connection for every function. Account login may use HTTPS, while voice, gameplay, files, or notifications depend on other services and transports.
FTP makes the distinction clear. A client connects to the control port and authenticates, then uses a separate connection for data. In passive mode, the server supplies another port. Successful login and failed file transfer are therefore entirely compatible outcomes.
Notifications can also need separate connections. Firebase Cloud Messaging documentation, for example, lists TCP 5228, 5229, 5230, and 443. Opening a web page does not test that entire set.
Renting an exit IP is also different from forwarding inbound ports to the customer's computer. If an application expects connections from outside, ordinary proxy access may be insufficient. That is a separate service capability, not something established by the word Dedicated.
When access can be expanded
For a nonstandard web port or an approved business task, a provider may offer customer verification and a separate permission. It may need the destination, transport, port, and intended activity. Approval can be limited to a particular account or task.
A permanent SMTP restriction does not become permission after submitting an identity document or buying a larger package. Identity verification and authorized operations are separate conditions. A service-level agreement does not automatically open ports either; expanded access must be specifically provided.
Legitimate email delivery has another service model: a mail API over HTTPS. The application submits the message to an email service, which handles delivery. The proxy's SMTP ports are not used. Access to the API must still be permitted, and both services' conditions still apply; an open 443 does not authorize prohibited messaging.
Running a private server can provide more control over the proxy software, but the hosting and external networks retain their restrictions. A seller's promise of “all ports open” is useful only when it identifies the transports, directions, and destinations covered.
What a proxy test establishes
An IP checker opened over HTTPS confirms that particular web connection. It does not test SMTP, SSH, UDP, or FTP's second connection.
An online port checker also normally connects from its own network. Its result describes the destination's availability to that checker, not the route through the customer's proxy.
A working IP and a service suited to the task are separate qualities. A browser may need only permitted web access. An application with other network functions depends on its particular destinations and transports. Those requirements determine whether the customer needs a different product, approved access, or a corrected configuration.